Use a layered approach: an invisible honeypot and time-trap first, then server-side verification, then a privacy-friendly challenge like Cloudflare Turnstile only if you still need it, plus a content-scoring layer such as Akismet for anything that slips through. Your first move today should take five minutes: enable a honeypot and minimum submission time on every public form, or switch off comments entirely if nobody actually uses them. Everything below walks through the settings, the ordering, and how to tell it’s working.
TL;DR:
- Most spam is blocked early by low-cost layers like honeypots, minimum time delays, and IP rate limiting, reducing reliance on paid third-party services.
- Disabling comments altogether is the simplest and most effective method if your site does not depend on reader engagement.
- For contact and lead forms, layering honeypots, JavaScript tokens, time delays, and optional challenge services drastically reduces spam without harming real user conversions.
- Monitoring and testing spam filters in staging sites ensures legitimate submissions are not accidentally blocked, with adjustments made based on ongoing data.
- Combining local checks with a content-scoring service like Akismet offers the best balance, but avoid overlapping or redundant spam detection layers to minimise costs and false positives.
Table of Contents
- What is WordPress spam protection, really?
- How do I stop WordPress comment spam?
- How do I protect contact and lead forms from spam?
- Should I add sitewide bot protection beyond forms?
- What’s the ideal layered defence stack to actually build?
- How do you test spam filters without losing real messages?
- How TTOY Digital handles this for client sites
- Do I need Akismet, or can local defences handle it alone?
- How should I manage spam blacklists and whitelists?
- Can WordPress user roles reduce your spam risk?
- Are there good alternatives to Akismet worth considering?
- How do I stop spam on WooCommerce reviews and checkout?
- Does spam protection slow down my website?
- Most spam advice treats symptoms, not the actual problem
- Want this handled without touching a settings menu?
- Sources
- FAQ
What is WordPress spam protection, really?
WordPress spam protection isn’t one plugin. It’s a stack of small, boring checks that each catch a slice of junk before it reaches your inbox, your comment queue, or your product reviews. Get the order right and most of it disappears without a visitor ever noticing.
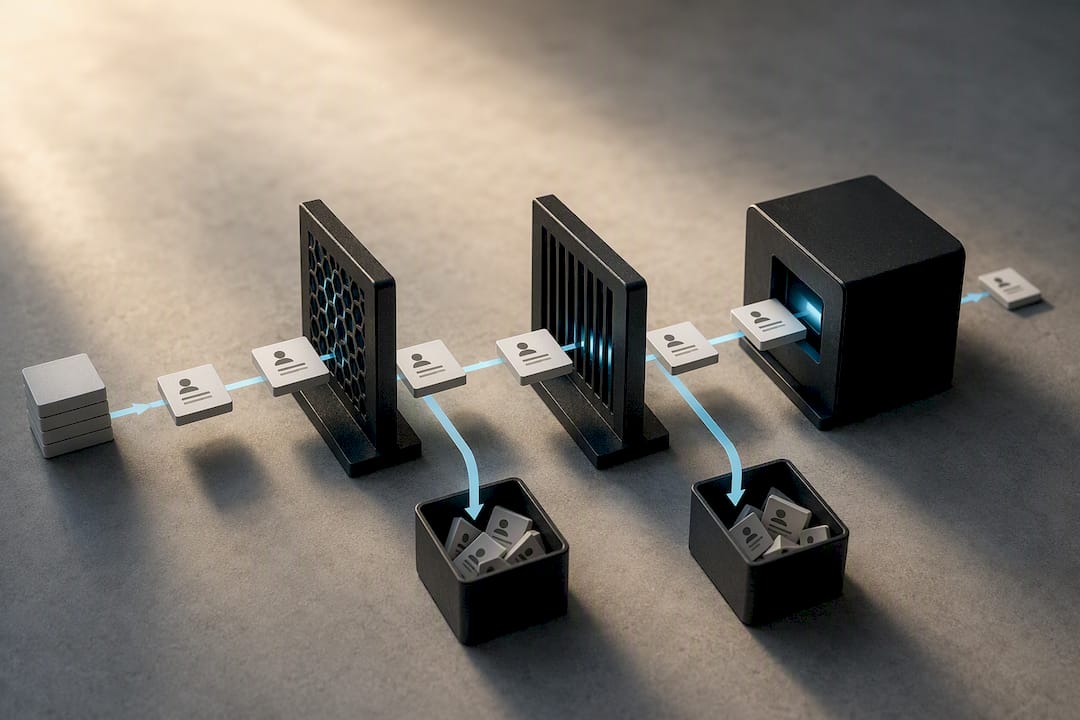
Think of it like sieves of different mesh sizes. You run the coarsest, cheapest sieve first, and only send what’s left through the finer, more expensive one. Here’s what sits in that toolbox:
- Honeypot fields: hidden inputs invisible to humans but irresistible to bots that fill in every field they find.
- Time-floor checks: a minimum time between page load and submission; bots submit in under a second, humans rarely do.
- JS tokens: a value set by JavaScript that proves a real browser rendered the page, not a script hitting your endpoint directly.
- IP and rate limits: capping how many submissions one address can make in a given window.
- Server-side token verification: cryptographically signed, anti-replay tokens that stop resubmitted or forged requests.
- Challenge services: Turnstile, hCaptcha, or reCAPTCHA, reserved for cases the earlier layers can’t resolve.
- Content scoring: a hosted service like Akismet checking the actual text against a spam corpus.
The order matters more than most owners realise. Run the free, local checks first: honeypot, time-floor, IP reputation. Only send what survives on to a paid or third-party service. This isn’t just tidiness. Layering cheap filters before expensive ones conserves API calls and keeps more of your visitors’ data on your own server rather than shipping it off to a scoring provider on every single submission.
Accessibility and privacy sit right alongside effectiveness in this decision. Visible CAPTCHAs can frustrate users on assistive technology and can shave 1 to 3 percent off form conversions depending on how aggressively they trigger. Turnstile and hCaptcha are generally gentler on both fronts than older reCAPTCHA implementations, which is why they’re the better default when a challenge becomes unavoidable.
How do I stop WordPress comment spam?
Comments are usually where spam shows up first and worst, because the endpoint is public, predictable, and heavily automated against. The fix depends entirely on whether you actually need comments.
If your site doesn’t rely on reader discussion, the cleanest option is to switch comments off site-wide. It’s blunt, but it’s also the single lowest-maintenance move available. Guidance from WPBeginner’s spam protection walkthrough is unambiguous on this: disabling comments removes the attack surface entirely rather than managing it, and it stops the slow database bloat that thousands of held or spam comments cause over time.
If comments matter to your business, here’s a workable sequence:
- Add a honeypot field to the comment form, hidden with CSS rather than
display:none(some bots specifically skip fields hidden that way). - Set a minimum time-to-comment, typically 4 to 8 seconds from page load, rejecting anything faster.
- Rate-limit by IP, capping repeat submissions from the same address within a short window.
- Layer in a scoring service like Akismet, which checks the comment text and metadata against its own spam corpus and can automatically discard the worst offenders before they ever reach your moderation queue.
- Review the held queue weekly, not daily. Spam accumulates fast, but reviewing too often wastes your time on obvious junk.
For moderation settings, discard genuinely obvious spam automatically, but hold anything with a first-time commenter’s link or an unfamiliar email address for manual approval. That single distinction protects you from losing a legitimate first-time customer enquiry disguised as a “comment.”
Watch for false positives from three sources: browser autofill tools that populate hidden fields unexpectedly, screen readers that navigate forms differently to a mouse user, and password managers that inject values faster than any human types. Test your honeypot with a screen reader before rolling it out, not after a complaint arrives.
Pro Tip: Rename your honeypot field something plausible like “website” rather than “leave_blank” or “spam_trap”, obvious names get stripped out by DOM-aware scraping bots before they ever submit the form.
How do I protect contact and lead forms from spam?
Contact and lead forms carry more weight than comments because every blocked submission is potentially a lost customer, not just a lost comment thread. That changes the calculus: you want to catch bots while giving real enquiries every possible chance to get through cleanly.
A solid starter stack for any lead form looks like this:
- Honeypot field, rotated in name and position occasionally so scrapers can’t hard-code around it.
- JavaScript-set nonce, a token only a real browser executing JS can generate, which instantly filters headless scripts that skip JS rendering.
- Time-floor check, usually 3 to 10 seconds depending on form length.
- Server-side verification of both the nonce and the time-floor before the submission ever reaches your inbox.
Tested together, this kind of layered setup pushes spam volumes right down. Splitforms’ comparison found a honeypot alone catches roughly 85 to 92 percent of basic form spam on lower-traffic sites, and a fully layered stack reduced spam to around 1 percent in their testing.
If you’re still seeing determined spam after that, that’s when Turnstile or hCaptcha earn their place, not before. Both are less invasive than classic reCAPTCHA checkboxes and don’t rely on the same tracking-heavy risk scoring. Some challenge services run mostly invisibly, only prompting a visible challenge when their signals are genuinely ambiguous. The trade-off is real, though: any visible challenge introduces some conversion risk, so treat it as a last resort for forms where every lead has real value, such as lead capture forms designed to generate quality enquiries, not a default you switch on everywhere.
For Contact Form 7 users specifically, NoCaptcha Spam Filter for Contact Form 7 is worth a direct look. It bundles a honeypot, cryptographic token signing, anti-replay nonces, and a configurable minimum submission time into one plugin, and it’s built to remain cache-safe, which matters if your host aggressively caches pages. You can set CF7NCSP_MIN_TIME directly in wp-config.php, and it’s worth tuning that value up from the 10 to 30 second recommended range if you notice genuine users submitting via keyboard shortcuts get blocked, since very fast legitimate completions can occasionally trip an aggressive floor.
Whatever stack you land on, don’t flip a challenge on and walk away. Monitor your conversion rate for a week or two after any change. If enquiries drop noticeably, loosen the time-floor or swap a visible challenge for an invisible one before assuming the spam problem is solved.
Pro Tip: Before adding any visible CAPTCHA, calculate what one lost enquiry is worth to your business. If a single missed lead costs more than months of manageable spam, that’s your answer on whether to add friction at all.
Should I add sitewide bot protection beyond forms?
Forms and comments aren’t the only doors bots knock on. Your login page, registration endpoint, and even your search function get hit by automated traffic too, and that traffic can slow your site down long before it manages to break in.
The /wp-login.php page deserves specific attention because it’s the single most probed URL on almost any WordPress install. Sensible defaults here:
- Rate-limit login attempts per IP address, locking out after a handful of failures within a short window.
- Enable two-factor authentication for every admin and editor account, not just the main owner login.
- Rename or restrict access to the login URL where your hosting setup allows it, cutting down blind automated attempts.
- Add a local proof-of-work challenge for repeat offenders rather than an external CAPTCHA, which keeps the check entirely on your own server.
That last option deserves a mention because it’s genuinely underused. ProofShield runs a small computational challenge in the visitor’s browser rather than sending anything to a third-party CAPTCHA service, covering login, comments, and generic forms without an external API key. It won’t stop a determined, well-resourced attacker, but for the noisy, low-effort automated traffic that makes up most bot activity, it’s an effective, privacy-respecting middle ground that avoids the cross-site fingerprinting concerns that come with some cloud CAPTCHA providers.
For genuinely high-volume attacks, plugin-level defences eventually hit their ceiling. That’s the point to consider a network-level firewall like Cloudflare’s WAF, which filters malicious traffic before it ever reaches your server, rather than after WordPress has already spent CPU cycles processing the request. If you’re running a small-business site with modest traffic, plugin-level rate limiting is usually sufficient. If you’re seeing thousands of automated login attempts a day, it’s time to escalate. Our overview of website security fundamentals covers where anti-spam sits within that broader picture.
What’s the ideal layered defence stack to actually build?
You don’t need every tool on day one. What you need is the right order, applied consistently, with room to add more only when the data says you need it.
A starter stack, buildable in 15 to 30 minutes on almost any WordPress site:
- Honeypot field on every public form, including comments.
- Minimum time-to-submit set between 4 and 10 seconds depending on form length.
- Akismet active on comments and contact forms, using its default settings.
- Basic rate limiting on
/wp-login.php. - Comments disabled entirely if you don’t genuinely need them.
For a hardened stack, suited to higher-traffic sites or ones that have already been targeted:
- Everything in the starter stack, plus a JS-set token verified server-side.
- IP reputation checks or a lightweight local rate limit across all public endpoints.
- A content classifier or AI-assisted filter, such as SpamAnvil, for catching more sophisticated, human-mimicking spam.
- Turnstile or hCaptcha reserved specifically for forms or login pages still seeing spam after the cheaper layers are in place.
- Two-factor authentication enforced for every privileged account.
The ordering isn’t arbitrary. Running the cheap, local checks first means most spam never reaches a paid or third-party service at all, which keeps your API costs down and your visitors’ data on servers you actually control.
Once the stack’s live, track three numbers: how much spam is being caught, how many false positives you’re finding in the discard pile, and whether your conversion rate on lead forms has moved. Check all three at 30 days, then again at 90. If false positives are near zero and spam volume has dropped sharply, leave the stack alone. If genuine leads are getting caught, that’s your signal to loosen a threshold, not tighten one.
Pro Tip: Set a calendar reminder to review your spam queue at 30 and 90 days after any change. Most owners only check when something breaks, by which point a genuine lead has usually already been lost.
How do you test spam filters without losing real messages?
Never tune a live anti-spam stack directly on production without a way to check what you’re actually catching. A staging copy of your site, or even just a test form pointed at a throwaway inbox, lets you fire test submissions through every layer before it touches real visitors.
Run through this before rolling any change out fully:
- Submit a deliberately fast, bot-like test through the form to confirm the time-floor and honeypot actually trigger.
- Submit a slow, human-paced test with a screen reader active to confirm nothing legitimate gets blocked.
- Check the held or discarded queue after both tests to see exactly where each submission landed and why.
- Roll the change to production only once both tests behave as expected, then monitor closely for the first week.
Once live, keep a simple log of what’s being caught and by which layer. Most hosting dashboards or plugins like Akismet already show a history of flagged submissions; glance at it weekly rather than letting it pile up unreviewed for months. Watch particularly for repeat offenders hitting the same endpoint. Repeated attempts from a narrow IP range often mean it’s time to add a rate limit rather than tolerate the noise.
If you discover a false positive, the recovery process is straightforward: pull the message from spam or trash, respond to the customer directly and apologise for the delay, then loosen the specific threshold that caught it. If a time-floor is catching fast typers, raise the floor slightly. If a honeypot is catching an autofill tool, adjust the field’s autocomplete attribute rather than abandoning the honeypot altogether.
How TTOY Digital handles this for client sites
Our own workflow follows the same shape every time: audit the current setup, apply the starter stack, monitor for two to four weeks, then harden wherever the data actually justifies it. We don’t install every available layer on day one, because most small-business sites don’t need it, and unnecessary friction costs you leads without stopping any real threat.
What changes case to case is the order of priorities. A site with an active comment section behind a niche blog needs a different balance to a service business whose entire lead flow runs through one contact form. We tune the stack around whichever endpoint actually matters most to that business’s revenue.
If you’d rather not manage this yourself, it’s exactly the kind of ongoing task WordPress maintenance exists for. We also flag related weak points while we’re in there. Our note on common WordPress security issues covers several that tend to sit next to spam problems, particularly outdated plugins and weak login policies.
Do I need Akismet, or can local defences handle it alone?
Akismet still earns its place for most sites, but it’s a content-scoring layer, not a substitute for the cheaper checks that should run before it. It works by checking submitted comments and contact-form entries against a global spam corpus, tagging status history on each comment and offering a discard option for the worst offenders so they never clutter your queue at all.
The reason to run local checks first isn’t distrust of Akismet. It’s efficiency. A honeypot and time-floor filter out the laziest, most automated spam for free, with zero latency and zero data leaving your server. What’s left after that, the more convincing, human-mimicking submissions, is exactly what a scoring service is built to catch. Sending everything to Akismet without any local pre-filtering works, but it means every piece of obvious junk still makes a round trip to a third-party API before being discarded.
For sites facing more sophisticated, AI-generated spam that reads convincingly human, a newer generation of open-source filters like SpamAnvil layer heuristics and rate-limiting with an AI-based verdict, running asynchronously in the background so it doesn’t add noticeable delay to the visitor’s experience. That’s a reasonable next step once a hosted scoring service alone stops feeling sufficient, rather than a replacement for it.
How should I manage spam blacklists and whitelists?
A blacklist blocks known bad actors outright: specific IP addresses, email domains, or keyword patterns that show up repeatedly in spam you’ve already caught. A whitelist does the opposite, letting trusted senders, existing customers, or verified partners bypass certain checks entirely.
Build your blacklist reactively rather than trying to guess it in advance. Every time you confirm a genuine spam pattern, whether that’s a recurring domain in the “website” field or a specific phrase pattern, add it to your filter rules. Most anti-spam plugins support this natively, and it takes seconds once you’re in the habit.
Whitelisting is where owners tend to get it wrong. It’s tempting to whitelist an entire email domain to stop a supplier’s messages getting caught, but that opens exactly the loophole a spammer will eventually find if that domain is ever spoofed. Whitelist specific addresses, not domains, wherever the option exists, and review the list every few months to remove anything no longer needed.
Keep both lists visible and documented somewhere your team can see them. A blacklist nobody remembers exists doesn’t get updated, and a whitelist nobody audits eventually becomes its own security gap.
Can WordPress user roles reduce your spam risk?
User roles matter here in a way most owners overlook. Every account with publishing or comment-moderation privileges is a potential entry point, and the more accounts with elevated access, the more surface area you’re managing.
Keep your role assignments tight. Give Contributor or Author roles to genuine content contributors only, and restrict comment moderation privileges to the smallest group that actually needs them. A Subscriber-only registration setup, if your site doesn’t need public sign-ups at all, removes an entire category of automated account-creation spam before it starts.
If your site allows open registration, WooCommerce stores in particular, watch for accounts created in bulk within short windows, often a telltale sign of automated sign-up bots rather than real customers. Pairing registration with the same honeypot and time-floor checks used on your contact forms cuts this down significantly, since the same bot infrastructure that spams forms usually spams registration endpoints too.
Are there good alternatives to Akismet worth considering?
Akismet isn’t the only hosted scoring option, and for some sites a competing service fits better, particularly where GDPR data-handling preferences or pricing structure matter more than brand recognition. CleanTalk is one of the more established alternatives, working on broadly similar principles: checking submissions against a shared spam database and returning a verdict before the entry ever reaches your queue.
The choice between services usually comes down to three things: how the service handles visitor data, how its pricing scales with your comment or form volume, and whether it integrates cleanly with the specific form plugin you’re already running. None of these third-party scoring services should be your only line of defence regardless of which you pick. They work best positioned exactly where Akismet sits in the stack described earlier: after the free local checks, catching what slips past a honeypot and time-floor.
If you’re evaluating a switch, don’t run two scoring services simultaneously on the same form. It doubles your API calls without meaningfully improving your catch rate, since both services are largely checking against overlapping spam patterns. Pick one, configure it properly, and let your local layers do the first pass of filtering regardless of which hosted service sits behind them.
How do I stop spam on WooCommerce reviews and checkout?
WooCommerce stores face two separate spam problems: fake product reviews and bot-driven checkout attempts, usually testing stolen card details in small increments.
Product reviews run through the same comment system as your blog, so the same defences apply directly: a honeypot on the review form, a time-floor, and Akismet or an equivalent scoring layer checking the review text itself. It’s worth requiring a verified purchase before a review can be submitted at all, which WooCommerce supports natively and which eliminates the majority of drive-by fake reviews without any extra plugin.
Checkout spam is a different animal and needs a different response. Card-testing bots submit many small transactions in rapid succession, trying to find a card number that clears. Rate-limiting checkout attempts per IP address helps, and most payment gateways offer their own fraud-detection layer that catches this pattern independently of anything WordPress-side. Combining a WordPress-level rate limit with your payment processor’s own fraud checks covers both ends of the problem, rather than relying on either alone.
Guest checkout is convenient for conversions but also the path of least resistance for automated abuse. If checkout spam becomes a persistent issue, consider requiring account creation with the same registration-level protections described earlier, accepting the small conversion trade-off in exchange for a meaningfully smaller attack surface.
Does spam protection slow down my website?
Done well, no. The cheapest and most effective layers, honeypots and time-floor checks, add no meaningful server load at all. They’re simple field checks and a timestamp comparison, processed in milliseconds against data already present in the form submission.
Where performance can actually suffer is further up the stack. Third-party scoring services and visible CAPTCHAs each introduce an external request, and every external request adds latency, however small, plus a dependency on that service’s own uptime. A page loading a CAPTCHA script from a third-party domain is also loading an extra render-blocking resource unless it’s deferred properly.
A few practical habits keep the performance cost low:
- Load CAPTCHA or challenge scripts asynchronously, never render-blocking in the page head.
- Cache pages normally; token-based plugins like NoCaptcha for CF7 are built to remain cache-safe, so this shouldn’t require disabling caching on form pages.
- Run AI-based content scoring asynchronously in the background where the plugin supports it, rather than holding up the page response while a verdict is calculated.
- Avoid stacking two visible challenges on the same form; each one adds its own script and its own delay.
The general rule holds across almost every layer discussed here: the checks that cost you nothing in performance, honeypots, time-floors, local rate limits, should always run first. Anything with a genuine performance or privacy cost earns its place only after the free layers have already done most of the work.
Most spam advice treats symptoms, not the actual problem
Most guides on this topic obsess over block rates and barely mention the cost of getting it wrong. That’s backwards for a small-business site. A missed enquiry from a genuine customer is almost always worse than an extra spam comment sitting in your queue for a week, yet most default advice pushes owners straight to visible CAPTCHAs because they feel more thorough.
They’re not, necessarily. A CAPTCHA that annoys a real customer into abandoning your contact form has cost you more than the spam it was meant to stop. The research here is consistent on this point: invisible layers like honeypots and time-floors catch the overwhelming majority of low-effort spam with zero friction, and the conversion risk only appears once you add a visible challenge.
What I’d tell any owner reading this: start cheap, measure honestly, and resist the urge to add a CAPTCHA the moment spam appears. Watch your discard queue for two weeks before deciding anything needs to change. If you’re still overwhelmed after the free layers are properly configured, that’s when a challenge or a managed service earns its place, not before.
— Chris
Want this handled without touching a settings menu?
Some WordPress maintenance plans include building a full spam protection stack, so you don’t have to configure honeypots and tune time-floors yourself. An engagement starts with an audit of your current forms, comments and login setup, then moves to installing the starter stack, tuning thresholds against your real traffic, and monitoring the results monthly rather than leaving it to drift.
The outcome we’re aiming for on every site is straightforward: a sharp drop in spam reaching your inbox, false positives kept close to zero, and your lead-form conversion rate untouched by the change. If spam is already flowing into a CRM or sales pipeline, pairing that clean-up with SmartFlowCRM means recovered leads land somewhere your team can actually act on them, rather than getting buried under junk.
WordPress Maintenance runs from £30 per month per site. Get in touch and we’ll audit your current setup and tell you exactly what’s worth fixing first.
Sources
For anyone wanting to dig further into specific implementation details, these are worth keeping close:
FAQ
What is the best spam blocker for WordPress?
There isn’t a single best option; the strongest results come from layering an invisible honeypot and time-floor with a scoring service such as Akismet. Contact Form 7 users specifically benefit from a dedicated plugin like NoCaptcha Spam Filter, which bundles several of these checks together.
How do I permanently block unwanted spam?
No single setting blocks spam permanently, because spam tactics keep evolving, but a layered stack comes closest. Combine a honeypot and minimum submission time with a content-scoring service, review your held queue regularly, and tighten specific rules as new patterns appear rather than expecting one plugin to solve it once and for all.
How can I stop receiving spam comments in WordPress?
If comments aren’t essential to your site, disabling them entirely is the most maintenance-free fix. If you need comments, add a honeypot field, a time-floor of several seconds, and a scoring service like Akismet, which can automatically discard the worst spam before it reaches your queue.
What is the best anti-spam software?
The strongest setup isn’t one piece of software but a stack: a honeypot and time-trap first, since these alone catch roughly 85 to 92 percent of basic spam, followed by a hosted scoring service and, only if needed, a privacy-friendly challenge like Turnstile or hCaptcha.
Does TTOY Digital handle WordPress spam protection for clients?
Yes, spam and comment-form protection is part of TTOY Digital’s WordPress Maintenance service, which runs from £30 per month per site. It covers auditing your current setup, installing a layered defence, and ongoing monitoring so thresholds stay tuned as spam patterns change.